Open Call #1
Open
- Date
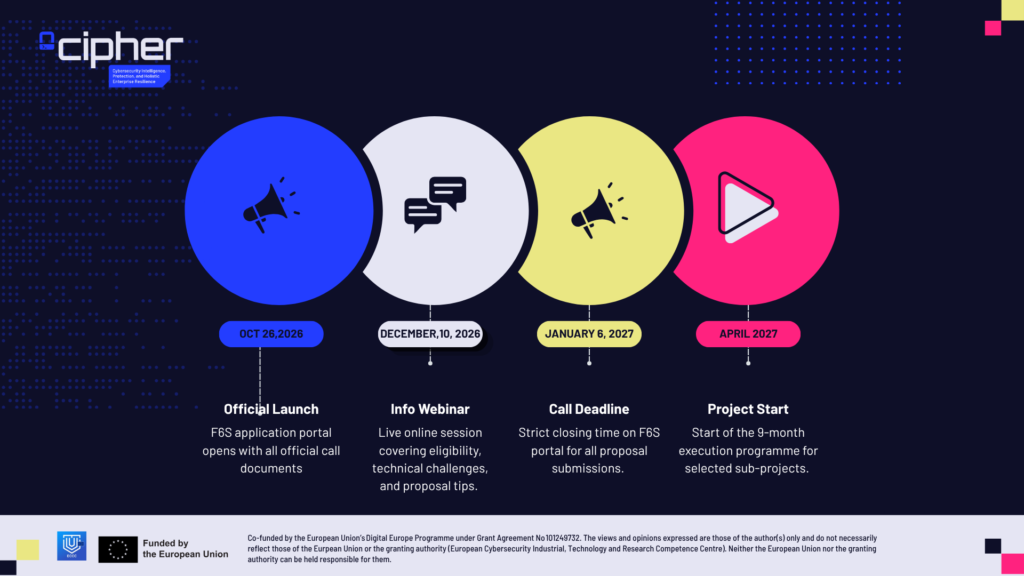
October 26, 2026 (13:00 CET)
- Deadline
January 6, 2026
(17:00 CET)
- Budget
Up to €60,000 per project
- Target Audience
More details below
Overview & Objectives
CIPHER Open Call #1 (OC1) is a 9-month cascade funding and technical implementation programme structured into 3 consecutive Sprints under the EU-funded CIPHER project. The initiative aims to enhance cybersecurity and information assurance across critical infrastructure sectors—with a primary focus on Operational Technology (OT) environments such as energy, transport, healthcare, and water management.
Selected third parties will work alongside assigned CIPHER mentors to test, validate, and expand CIPHER’s collaborative, “available-as-a-service” testing facility and cyber-range platform across three operational modes: Knowledge, Testing, or Range/Environment.
Programme benefits:
Equity-free cascade funding: A maximum grant of up to €60,000 per project (covering 50% co-funding of total eligible costs) disbursed in 3 milestone-based lump-sum payments (20% pre-financing in Sprint 1, 40% in Sprint 2, and 40% in Sprint 3).
Technical mentorship & platform access: Dedicated guidance from CIPHER technical mentors, access to isolated testing environments, scoped credentials, and specialised SaaS components (e.g., Wazuh XDR SaaS, immutable S3 WORM storage, and the Risk Monitoring Bundle).
Ecosystem visibility: Participation in the official CIPHER Demo Day, direct networking with European cybersecurity leaders, and dedicated promotional support from the CIPHER dissemination team.
Eligibility & Funding details
- Legal entity status: Single legal entities or micro-consortia (up to 3 partners) established in EU Member States (including overseas territories) or EEA countries (Norway, Iceland, Liechtenstein).
- Technology readiness & target profiles: Startups, SMEs, RTOs, or mid-caps offering products or solutions at Technology Readiness Levels (TRL) 6 to 8. Target profiles include vulnerability management specialists, SOC/detection engineers, critical infrastructure operators, DevSecOps experts, and certified NIS2/IEC 62443 compliance auditors.
- Consortium composition rules: If applying as a consortium, the group must include a mandatory Technology Provider and a mandatory End-User / Technology Adopter, with an optional Certified Cybersecurity Auditor.
- EU control restrictions: Non-public applicants must be EU-controlled and submit a mandatory Ownership Control Declaration (Annex 4) signed via Qualified Electronic Signature (QES).
Reference Documents
Annex 1: Guide for Applicants
Annex 2: Technical Requirements
Ownership and Control Assessment (OCA) Procedure
Templates
Annex 3: Technical Proposal Template
CIPHER FSTP Budget Template
Annex 4: Ownership Control Declaration (OCD)
Timeline & Selection Process